


Composio Review 2026: The Execution Layer That Lets AI Agents Actually Act
Composio review 2026: managed auth, MCP, dynamic tool discovery, sessions, and triggers across 1,500+ apps — plus the May 2026 security incident that turned this infrastructure layer's threat model into a real test case.
📋 Table of Contents
Composio review 2026: an AI agent that can only talk is still just a chatbot. The interesting part starts when it can open Gmail, update Salesforce, create a Linear issue, and send a Slack message — on behalf of the right user, without that user's OAuth token ever passing through the agent itself. That's the problem Composio sits between an AI agent and the software it needs to control, handling tool discovery, authentication, permissions, execution, sessions, and triggers across more than 1,500 apps.
But there's a harder question underneath that pitch. If you become the layer holding the keys to an agent's real-world actions, security isn't a feature anymore — it's the product. Composio learned that the hard way in May 2026, when an attacker used LLM-assisted exploit patterns to compromise an internal agentic tool and expose a small percentage of connected credentials. This review covers both halves honestly: a genuinely capable execution layer, and a company that had to rebuild parts of its security architecture in public this year.

What Composio Does
Dynamic tool discovery
Instead of loading thousands of tool schemas into an agent's context up front, Composio's Tool Router (GA after an October 2025 beta) searches for and surfaces only the tools relevant to the current request — solving a real context-bloat problem at scale.
Managed authentication
Composio handles OAuth, token storage, and refresh so credentials never pass through the application or the model itself — accounts are resolved by session and user identity, not by arguments the model controls.
Multi-user, multi-account architecture
Built for products with thousands of end users, each with their own connected accounts — the model's own outputs don't determine which credential gets used, the session context does.
MCP gateway
Works as an MCP server for Claude, ChatGPT, Cursor, Codex, and other MCP clients, exposing a small set of meta-tools for discovery and execution rather than dumping the full 1,500-app catalog into every client.
Triggers
Event-driven automation in the other direction — a new Gmail email or CRM update can wake an agent, which then acts and continues the workflow, unifying webhook-style events across CRM, commerce, and support tools.
Shared Connections (new, Sept 14 2026)
Lets a team share one company-owned account (like a shared inbox) across approved users without distributing the underlying password, using allow/deny lists — private connections stay private by default.
Pricing
| Plan | Price | Includes |
|---|---|---|
| Free | $0 | 100,000 tool calls/mo, 50,000 trigger events/mo, 3 team members, unlimited connected accounts, hard-capped (no surprise overage) |
| Pro | $29/mo | $29 usage credit (doesn't roll over), unlimited team members, spend controls, add-ons |
Beyond the base plans, costs stack across several separate meters: tool-call overage runs $0.0003/call after the free allowance (100,000 extra calls ≈ $30), triggers cost $0.003/event past 50,000/month, "premium" tools that proxy paid third-party providers (web search, browser automation, Google Maps) add roughly the provider's cost plus a 5% Composio fee, and Composio's own sandboxed LLM execution runs $3.75/1M tokens after a 1M free allowance — none of which applies if you're calling your own model provider directly. Zero Data Retention is a paid add-on at $0.0001/tool call and $0.0005/trigger event. This pricing structure took effect for new signups on August 15, 2026; customers who signed up earlier kept legacy pricing through the end of 2026, though premium-tool charges apply to everyone starting September 10. If you find older articles quoting $19 or $49/month, that's outdated pricing.
Learning Curve
This is not a plug-and-play Zapier alternative. Composio asks you to think in terms of sessions, project/organization boundaries, per-toolkit permission scopes, and — if you're serious about production use — which credential-storage model (Composio-managed vs. customer-managed KMS) fits your compliance requirements. Teams with 1–2 integrations to wire up genuinely don't need this; teams building an agent product with real multi-user auth requirements will find the learning investment pays off quickly, because the alternative is building the same identity-and-execution layer themselves.
Pros & Cons
Composio vs. the Field
Purpose-built for AI agents: dynamic tool discovery, multi-user identity, session-based credential resolution, and policy enforcement outside model reasoning — the category this review is evaluating.
Built for human-triggered or rule-based business workflows ("when X happens, do Y") — not designed around an LLM deciding what to do next and needing identity-aware execution.
A transport protocol, not a managed platform — doesn't inherently solve multi-user credential lifecycle, policy enforcement, or audit logging on its own. Composio can sit behind MCP rather than compete with it.
Security & the May 2026 Incident
On May 21, 2026, Composio disclosed unauthorized access to internal systems. According to the company's own bulletin, an attacker used LLM-assisted exploit patterns to compromise an internal agentic tool used to monitor infrastructure and report connector failures, then moved through automated remediation systems to escalate privileges and ultimately expose a subset of connected credentials — Composio reported roughly 0.3% of total active connections affected, with GitHub (around 5,001 connections) the largest single category, alongside smaller numbers across Gmail, Jira, HubSpot, Linear, Notion, Slack, and others.
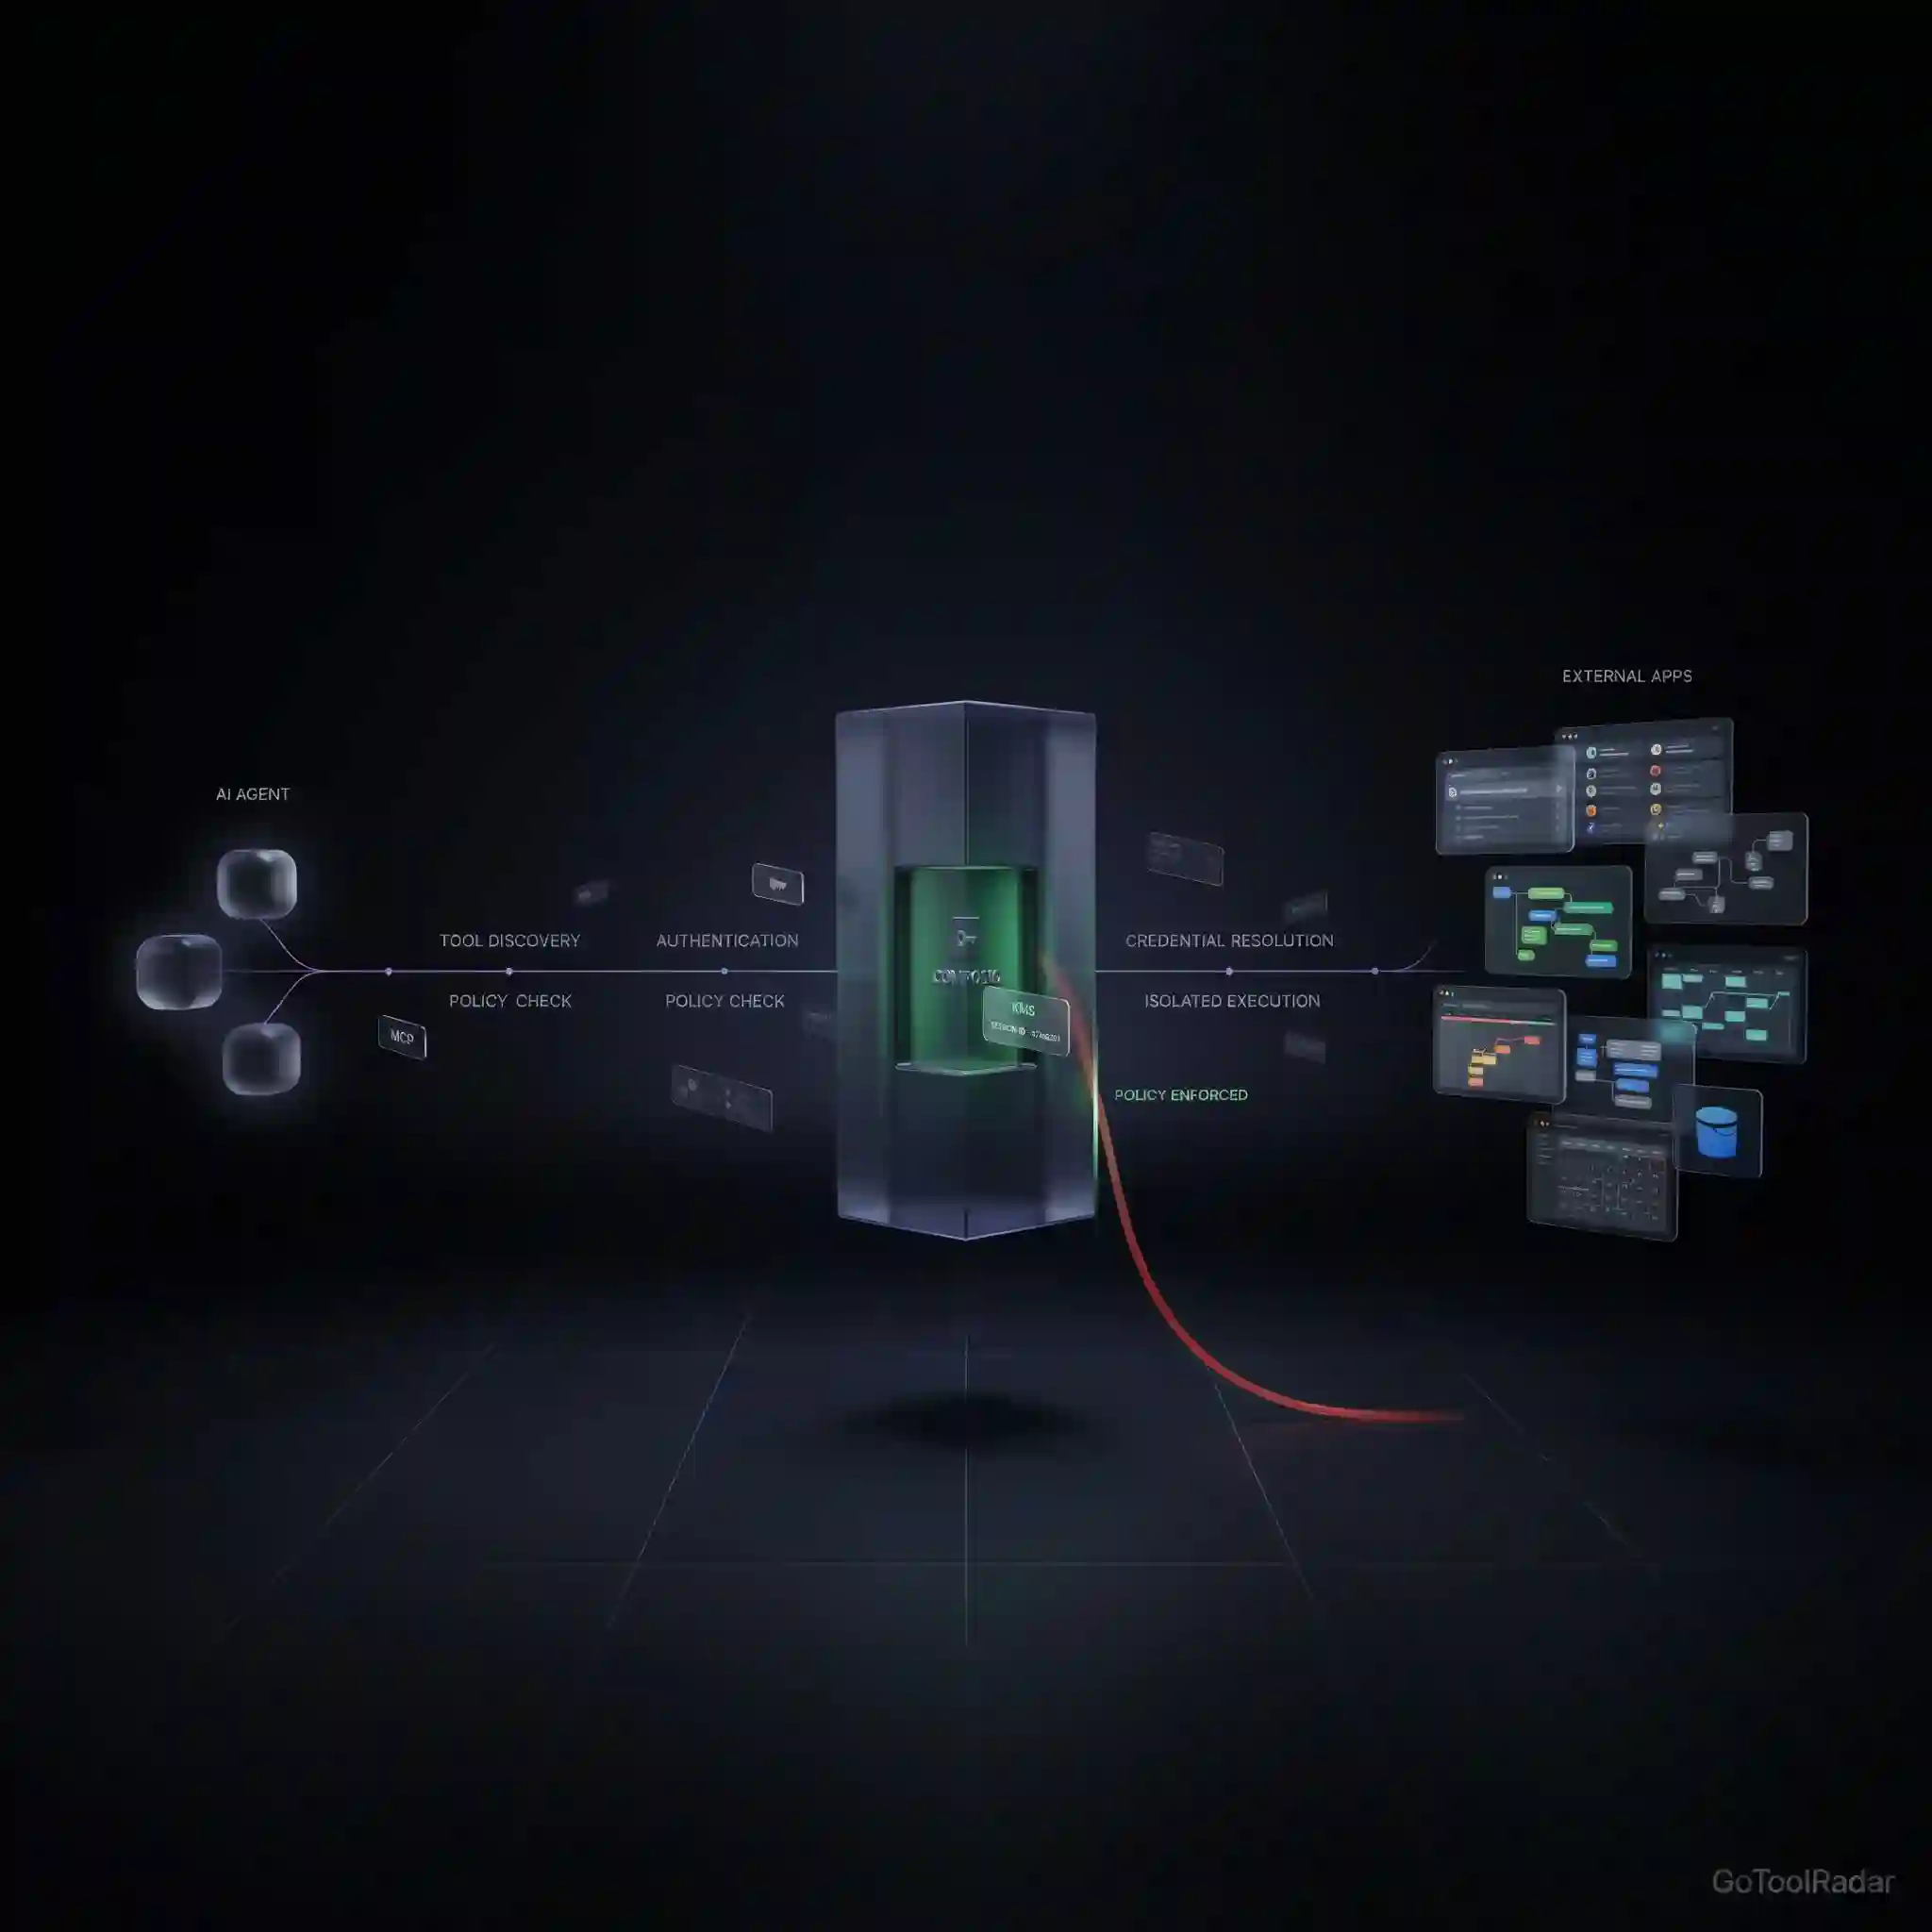
What makes this worth more than a footnote is the nature of the attack: a company building infrastructure for AI agents was compromised through a path that ran directly through its own internal agentic tooling. Composio's response was substantive rather than cosmetic — all affected GitHub tokens were revoked as a precaution, affected users were notified, credentials and encryption keys were rotated, and the company published a technical breakdown of a rebuilt execution architecture in September: requests now flow through authentication, a policy check, token resolution, and an isolated execution container before reaching a third-party API, with credentials decrypted only momentarily inside that isolated runtime — never returned to the calling application or exposed to the model's context.
A separate reliability incident in April 2026 is worth noting too, if only because it happened in the same window: a stalled cleanup job let a trigger-processing database table grow unbounded, cascading into roughly 36 hours of webhook trigger outages affecting an estimated 700 customers. Neither incident alone would necessarily be disqualifying — most infrastructure companies have a bad month eventually — but for a product whose entire value proposition is holding the keys to an agent's real-world actions, this year's incident history is material context, not a side note, for anyone connecting production credentials.
Who Should Use It
Ideal user: a team building an AI agent product with real multi-user requirements — thousands of end users, each needing their own connected accounts, where building OAuth lifecycle, permissions, and audit logging in-house would otherwise become a company of its own.
Look elsewhere if: you need one or two personal integrations for a side project (a lighter tool or a direct MCP server is simpler), or you're not yet comfortable giving a third party custody of production OAuth credentials without reviewing their 2026 incident history first.
Expert Editorial Opinion
The most useful lens for Composio isn't "how many integrations does it have" — competitors can build long integration lists too. The actual differentiator is the identity-and-execution layer underneath: who is this agent acting for, which account, which action, is it allowed, execute, log. That's the part that's genuinely hard to build production-grade, and it's why companies like AWS, Glean, and Browser Use reportedly use Composio behind their own agent products rather than building this layer themselves.
It's also exactly why this review can't treat the May 2026 incident as a footnote. A tool-integration company getting breached is bad. An agent-infrastructure company getting breached through its own internal agentic tooling is a preview of a threat model the entire industry is going to have to take seriously — attackers using LLM-assisted techniques against the automation layers companies build to manage their own systems. Composio's public, detailed response to that incident is genuinely better than what most vendors do after a breach, and it should factor into the evaluation — but it doesn't erase the fact that it happened.
The other honest caveat sits in Composio's own benchmark data. A company confident in its execution layer publishing a benchmark where several stateful, multi-step tasks score under 50% — some at 0% — is a credibly humble move, and it's a useful reminder that Composio makes execution possible; it doesn't make the underlying model reliable. If an agent picks the wrong tool, mis-fills a parameter, or loses track of state across steps, Composio's infrastructure won't rescue that on its own.
Taken together: this is a serious, well-engineered answer to a real problem, priced reasonably for teams that need it, with a security and reliability history in 2026 that demands eyes-open evaluation rather than a blanket recommendation. That combination — genuinely valuable architecture, genuinely material incident history — is precisely why this scores as competent-but-compromised rather than an easy top-tier pick.
Final Verdict
Composio solves a genuinely hard problem — multi-user identity, credential lifecycle, and policy-enforced execution for AI agents — with real architectural depth and unusually transparent incident disclosure. The score reflects that alongside two things that can't be waved away: a May 2026 security incident that exposed a portion of connected credentials through the company's own internal agentic tooling, and the company's own published benchmark showing real limits on complex, stateful tool-use tasks. This is a strong fit for teams that need exactly what it offers and are evaluating with full knowledge of its 2026 history — not a default pick for every agent project.
| Dimension | Weight | Score /10 | Why | |---|---|---|---| | Technical quality | 30% | 6.5/10 | Genuinely useful architecture (discovery, sessions, auth), but Composio's own benchmark shows real gaps on complex, stateful tool-use tasks | | Price-to-value | 25% | 7.0/10 | Generous, hard-capped free tier and reasonable overage rates, offset by cost spread across several separate pricing meters | | Maturity & documentation | 20% | 5.5/10 | Well-documented product, but a May 2026 security incident and a separate April 2026 reliability outage are direct maturity concerns within the same year | | Ceiling & flexibility | 15% | 9.5/10 | Model/framework-agnostic, self-hosting, customer-managed KMS, MCP compatibility, and multi-user architecture give it a very high ceiling | | Honesty of positioning | 10% | 8.5/10 | Published detailed incident bulletins, indicators of compromise, and a technical rebuild write-up — genuinely above-average transparency for a breach | Weighted total: (6.5×0.30) + (7.0×0.25) + (5.5×0.20) + (9.5×0.15) + (8.5×0.10) = **7.075/10**, rounded to **7.1/10** — Score band: 7.0–7.9, "Competent but compromised — a strong fit for a specific kind of user, not an automatic pick for every team handing over production credentials."❓ Frequently Asked Questions
🔗 Related ToolRadar Reviews
Official source: Composio. Given the pace of change here — new pricing since August, Shared Connections since September 14, and an evolving security architecture — verify current terms directly before connecting production credentials.
Comments
Post a Comment